5 min read
IAM Chapter 5: OAuth 2.0, Part 2
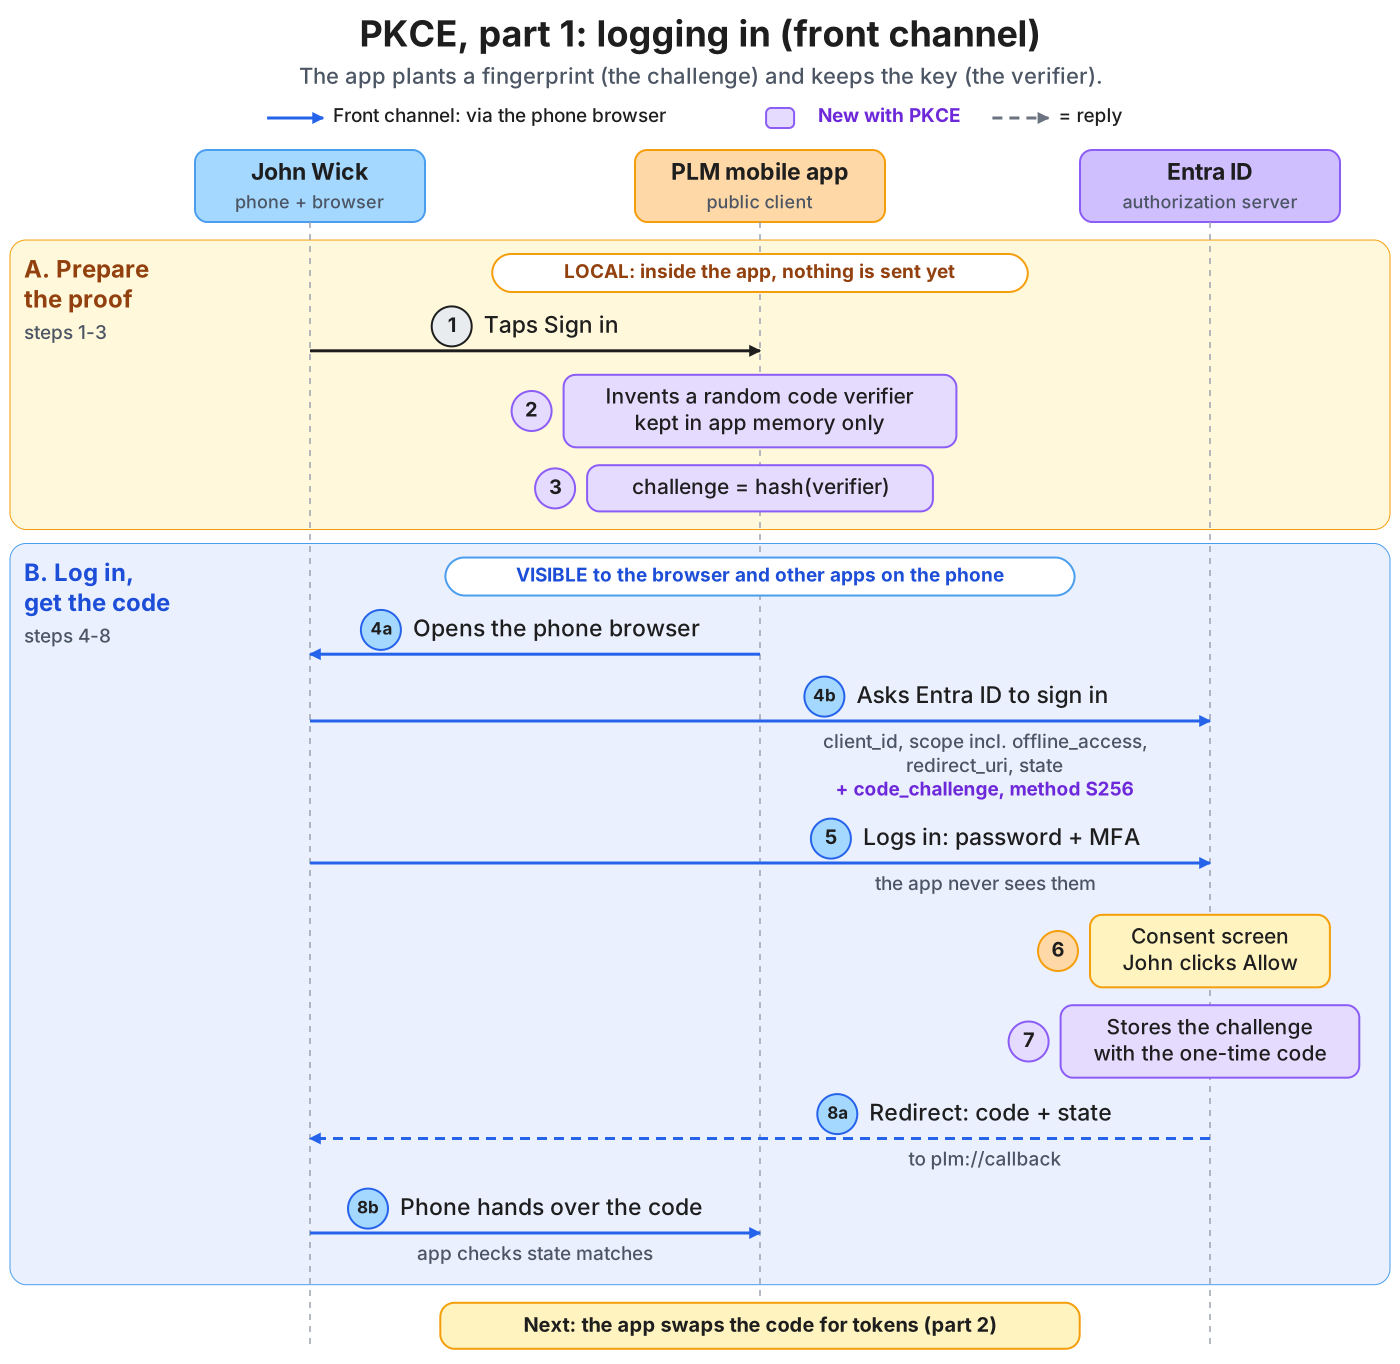
A mobile app cannot hide a client secret, so a stolen authorization code becomes free tokens. PKCE fixes this with a fresh, one-time proof invented at the start of each login — walked as diagrams, plus the full flow in one picture.