Blog
IAM Chapter 8, Part 2: Blast Radius
On this page
Part of the IAM study series.
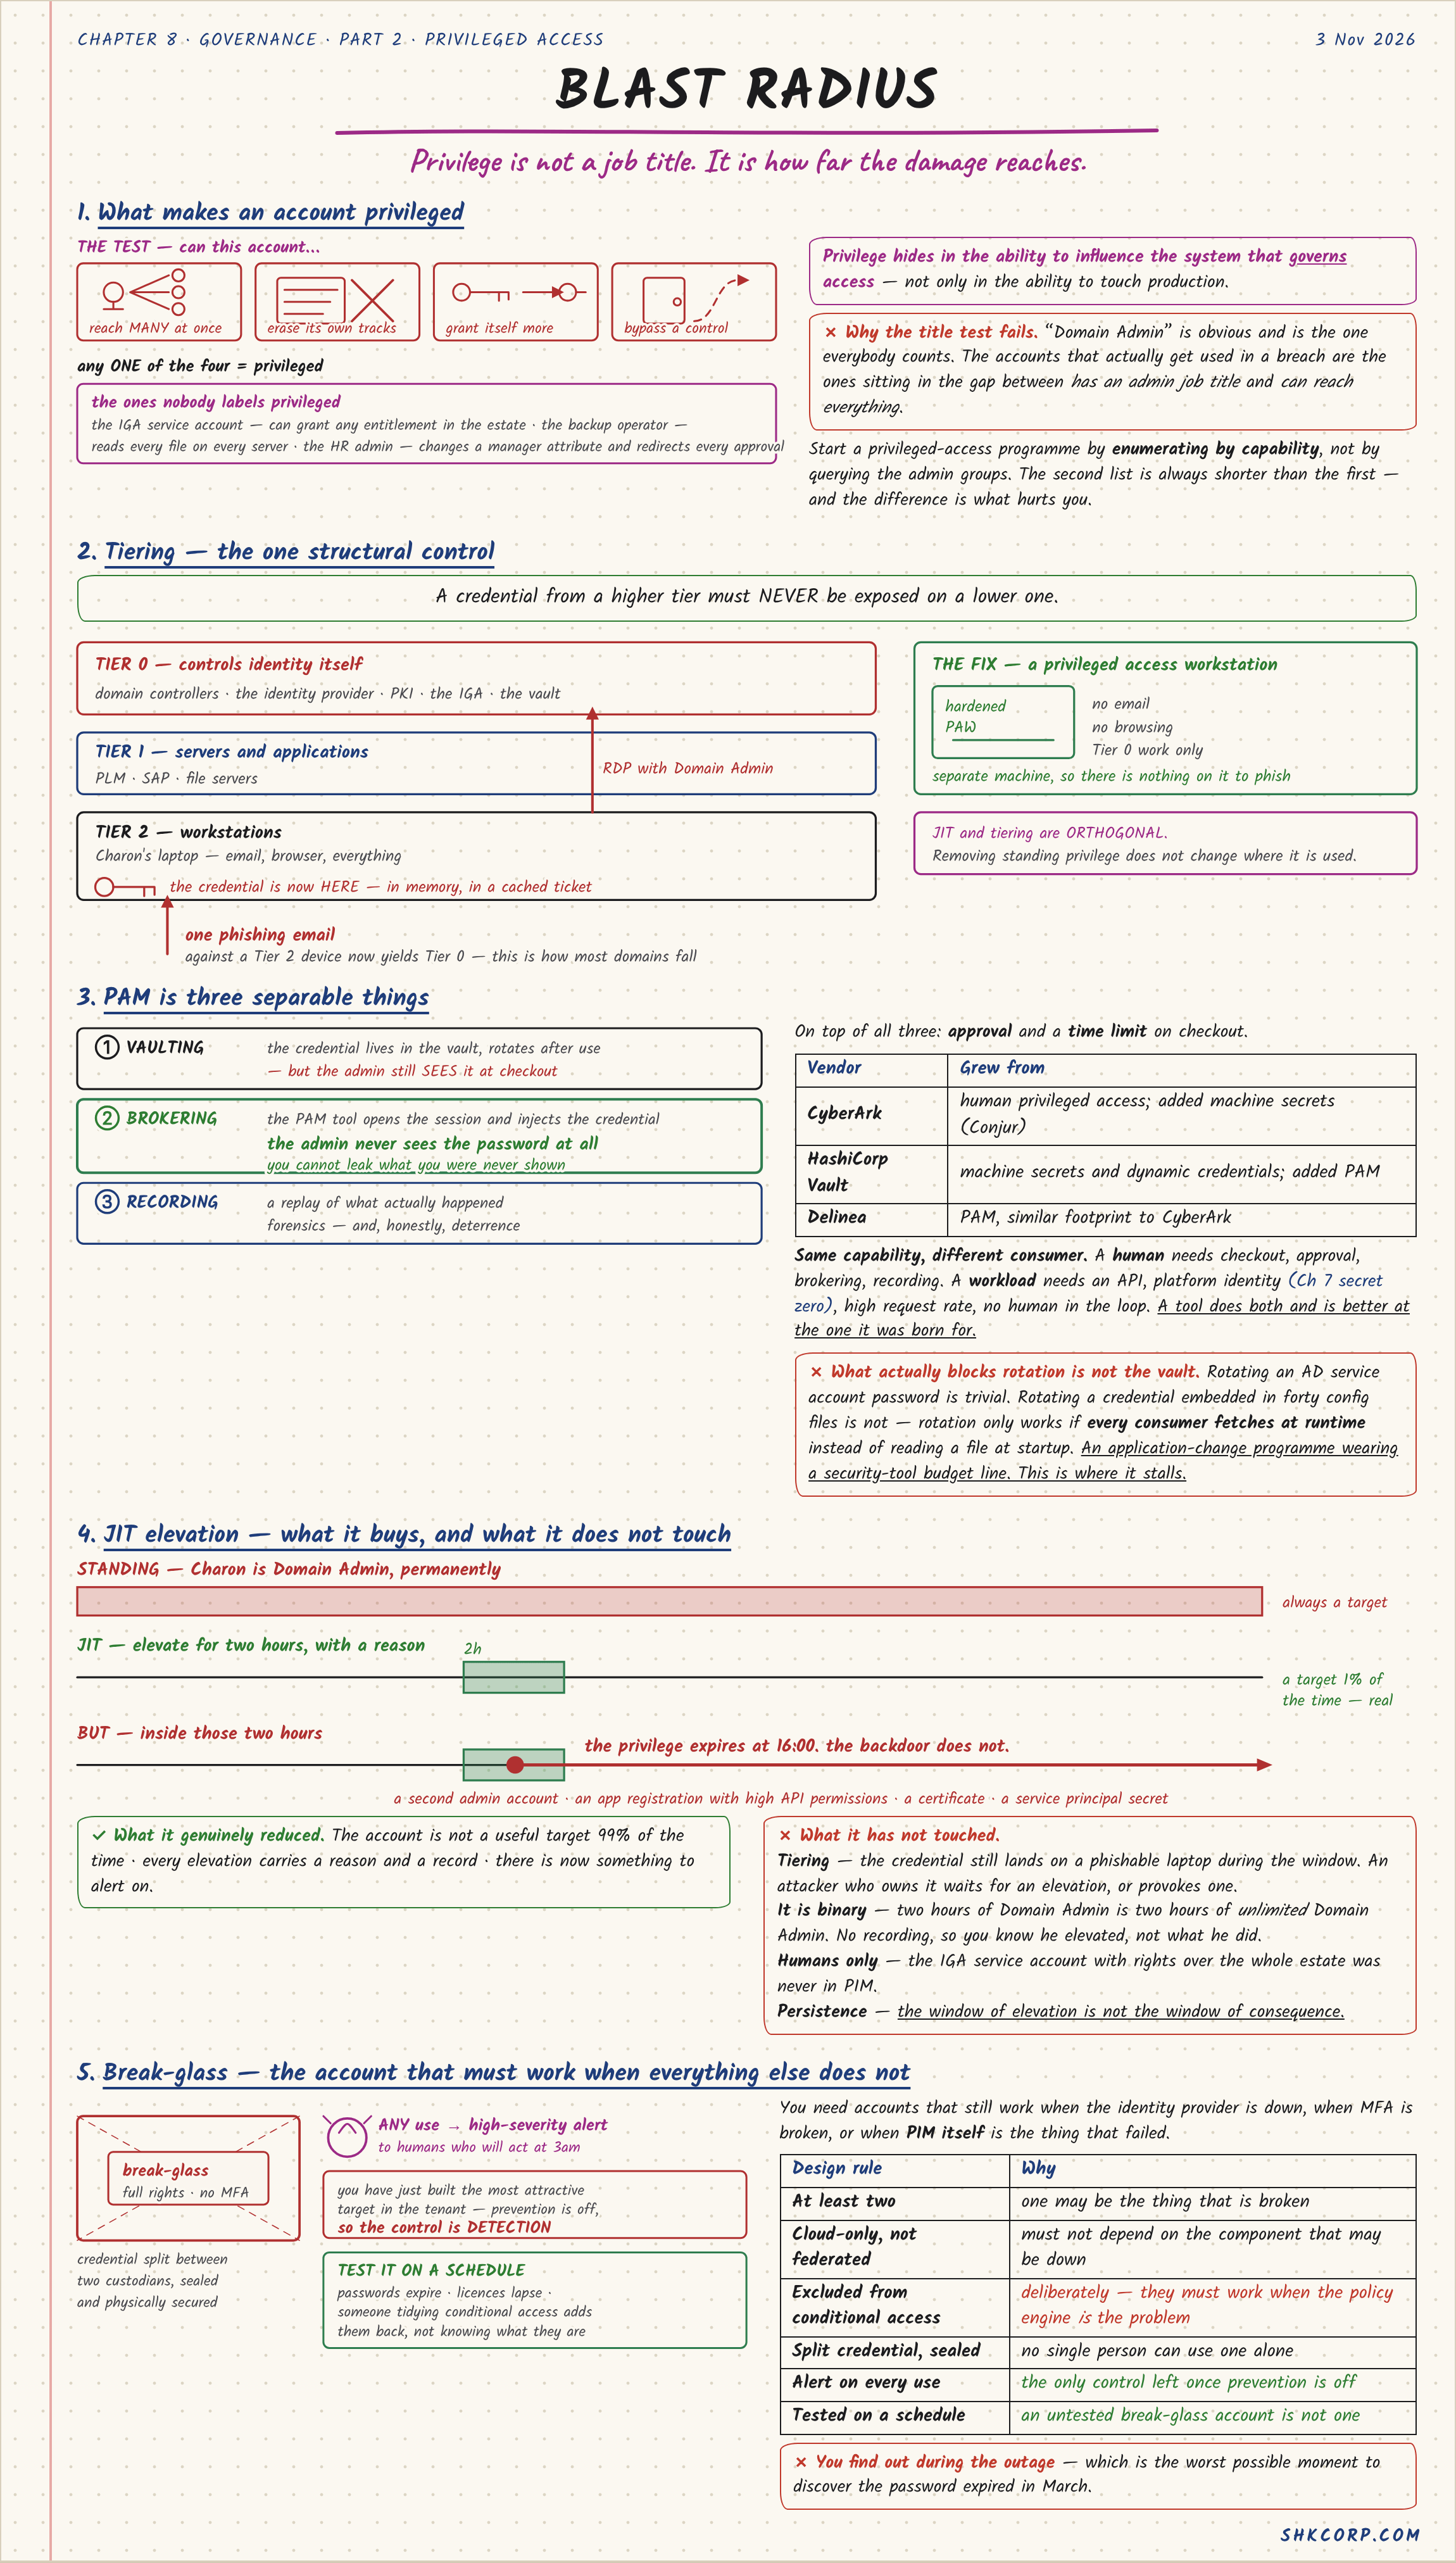
Privilege isn't a job title. It's how far the damage reaches.
1. What Makes an Account Privileged
The test: can this account…
- reach many systems at once?
- erase its own tracks?
- grant itself more?
- bypass a control?
Any one of the four means it's privileged.
The ones nobody labels privileged: the IGA service account (it can grant any entitlement in the estate), the backup operator (reads every file on every server), the HR admin (changes a manager attribute and redirects every approval). Privilege hides in the ability to influence the system that governs access, not only in the ability to touch production.
Why the title test fails. "Domain Admin" is obvious and is the one everybody counts. The accounts that actually get used in a breach sit in the gap between has an admin job title and can reach everything.
Start a privileged-access programme by enumerating by capability, not by querying the admin groups. The second list is always shorter than the first, and the difference is what hurts you.
2. Tiering: The One Structural Control
A credential from a higher tier must never be exposed on a lower one.
| Tier | Controls | Examples |
|---|---|---|
| Tier 0 | Identity itself | Domain controllers, the identity provider, PKI, the IGA, the vault |
| Tier 1 | Servers and applications | PLM, SAP, file servers |
| Tier 2 | Workstations | Charon's laptop: email, browser, everything |
Charon RDPs into a domain controller from his laptop with Domain Admin. The credential is now on Tier 2, in memory, in a cached ticket. One phishing email against a Tier 2 device now yields Tier 0. This is how most domains fall.
The fix is a privileged access workstation (PAW): a hardened, separate machine with no email, no browsing, and Tier 0 work only. There's nothing on it to phish.
JIT and tiering are orthogonal. Removing standing privilege doesn't change where it's used.
3. PAM Is Three Separable Things
- Vaulting. The credential lives in the vault and rotates after use. But the admin still sees it at checkout.
- Brokering. The PAM tool opens the session and injects the credential, so the admin never sees the password at all. You can't leak what you were never shown.
- Recording. A replay of what actually happened: forensics, and honestly, deterrence.
On top of all three: approval and a time limit on checkout.
| Vendor | Grew from |
|---|---|
| CyberArk | Human privileged access; added machine secrets (Conjur) |
| HashiCorp Vault | Machine secrets and dynamic credentials; added PAM |
| Delinea | PAM, a similar footprint to CyberArk |
Same capability, different consumer. A human needs checkout, approval, brokering and recording. A workload needs an API, platform identity (Chapter 7's secret zero), a high request rate, and no human in the loop. Each tool does both, and is better at the one it was born for.
What actually blocks rotation isn't the vault. Rotating an AD service account password is trivial. Rotating a credential embedded in forty config files is not: rotation only works if every consumer fetches at runtime instead of reading a file at startup. That's an application-change programme wearing a security-tool budget line, and it's where rotation stalls.
4. JIT Elevation: What It Buys, and What It Doesn't Touch
- Standing: Charon is Domain Admin, permanently. Always a target.
- JIT: he elevates for two hours, with a reason. A target 1% of the time, which is a real improvement.
- But inside those two hours: a second admin account, an app registration with high API permissions, a certificate, a service principal secret. The privilege expires at 16:00. The backdoor doesn't.
What it genuinely reduced: the account isn't a useful target 99% of the time, every elevation carries a reason and a record, and there's now something to alert on.
What it hasn't touched:
- Tiering. The credential still lands on a phishable laptop during the window. An attacker who owns it waits for an elevation, or provokes one.
- It's binary. Two hours of Domain Admin is two hours of unlimited Domain Admin. With no recording, you know he elevated, not what he did.
- Humans only. The IGA service account with rights over the whole estate was never in PIM.
- Persistence. The window of elevation isn't the window of consequence.
5. Break-Glass: The Account That Must Work When Everything Else Doesn't
You need accounts that still work when the identity provider is down, when MFA is broken, or when PIM itself is the thing that failed. A break-glass account has full rights and no MFA. You've just built the most attractive target in the tenant, and prevention is off, so the control is detection: any use triggers a high-severity alert to humans who will act at 3am.
| Design rule | Why |
|---|---|
| At least two | One may be the thing that's broken |
| Cloud-only, not federated | Must not depend on the component that may be down |
| Excluded from conditional access | Deliberately: they must work when the policy engine is the problem |
| Split credential, sealed | No single person can use one alone (two custodians, physically secured) |
| Alert on every use | The only control left once prevention is off |
| Tested on a schedule | An untested break-glass account isn't one |
Test it on a schedule. Passwords expire, licences lapse, and someone tidying conditional access adds them back in, not knowing what they are. Otherwise you find out during the outage, which is the worst possible moment to discover the password expired in March.
What Breaks in Practice
| Mistake | What goes wrong | Fix |
|---|---|---|
| Counting admin groups | Misses the IGA, backup and HR accounts | Enumerate by capability |
| Tier 0 credentials on laptops | One phish yields the domain | Tiering and PAWs |
| Vaulting without brokering | The admin still sees and can leak the password | Inject credentials into brokered sessions |
| Buying a vault to fix rotation | Credentials stay baked into config files | Make consumers fetch at runtime |
| Treating PIM as done | Backdoors outlive the window; service accounts excluded | Tiering, recording, non-human coverage |
| Untested break-glass | Fails during the outage | Test on a schedule, alert on every use |
🔴 CHECKPOINT: Study Notes
← Previous: What Nobody Removes · Back to the series start · Next: The Border Is the Person →